See your entire environment.
Simulate the attack. Price the risk.
Onek.ai keeps a live model of your infrastructure — systems, people, access and third parties — and lets you ask it the questions a diagram can't answer: what breaks if this goes down, who can actually reach that, and what it costs. Then it tells you what to fix first.
No signup, no sales call. The demo is the real product on a seeded enterprise environment — open it and break something.
Onek.ai Joins the NVIDIA Inception Program
Onek.ai is a member of NVIDIA Inception, the program that supports startups building with accelerated computing and AI. It gives us NVIDIA technical expertise, developer tools and go-to-market resources as we scale the compute behind Onek.ai's risk simulation, graph analytics and on-prem AI. It is not an investment or an endorsement — it is access, and here is what we are doing with it.
Bigger ensembles, faster
Onek.ai's Monte Carlo and agent-based engines run today on ordinary CPUs. With NVIDIA's tooling we're moving them onto GPUs, so hundred-thousand-run ensembles over very large twins finish while you're still looking at the screen.
Graph analytics at estate scale
Centrality, community and anomaly detection already run across infrastructure, identity, customer and vendor graphs. Acceleration is what lets that keep up as twins grow past tens of thousands of nodes.
Fully on-prem AI
Onek.ai Assist is bring-your-own-AI and already runs against local models. NVIDIA's stack gives us a supported path to GPU-backed inference inside your own data center — so nothing leaves.
This is Onek.ai — not a mock-up
Every screen below is the real platform, running on a seeded enterprise environment you can open right now. No signup.
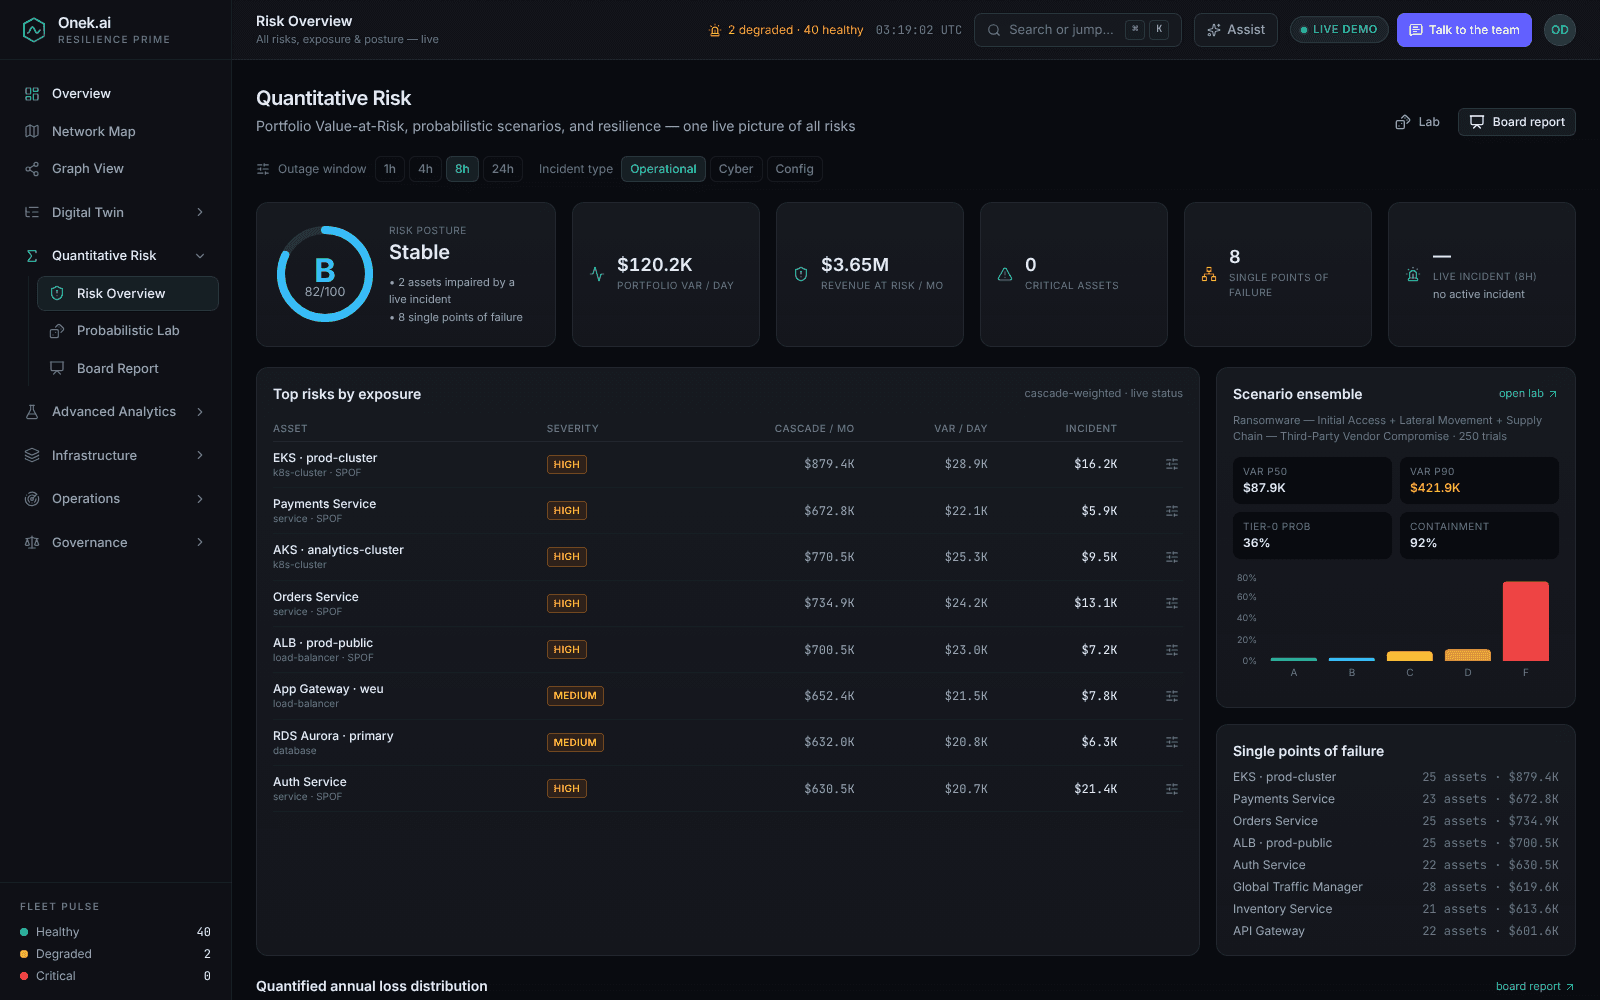
Portfolio Value-at-Risk, live
Top risks ranked by dollar exposure — cascade-weighted, with VaR per day and per incident, single points of failure, a seeded Monte Carlo ensemble and a board-ready report one click away.
Why disconnected security tools fail to answer the real question
Most security and IT teams run on five tools that don't talk to each other: an inventory here, a SIEM there, a spreadsheet of risks, a GRC binder, and a remediation backlog nobody can rank.
They disagree with each other, and none of them answers the only question leadership asks: “If we get hit, what does it cost us — and what should we fix first?”
Onek.ai collapses that stack into a single, living model of your environment. Instead of static diagrams and after-the-fact reports, you get a digital twin that updates from real telemetry, runs probabilistic attack simulations, and expresses risk in the language the board understands — money.
A digital-twin platform that unifies asset inventory, live network mapping, attack simulation, quantitative risk, compliance, and remediation prioritization.
Onek.ai pulls telemetry from across your stack and assembles it into one continuously updated graph: systems, people, access, data flows, dependencies. Then it puts that graph to work. Where are we exposed? What could an attacker reach from here? What would an outage of this cost? Are we meeting our obligations? What do we fix next? One model, and it answers all five.
Built around the financial decision
Six capabilities on one continuously updated model, arranged so the dollar figure decides what you look at, what you simulate and what you fix.
Quantitative Cyber Risk
Risk in dollars — the signal everything else is organized around.
Value at Risk (VaR) — Per-asset revenue, cost, and customer exposure roll up into portfolio-level value at risk.
Monte Carlo loss modeling — PERT/Beta marginals with a Gaussian copula produce p5–p99 loss, CVaR, and exceedance curves.
Board-ready reporting — An interactive risk overview and probabilistic lab, with exportable board PDFs.
The Living Digital Twin
A continuously updated model of IT, OT, people, and third parties.
Live network map & Graph View — A map that reacts to real traffic, plus blast-radius, shadow-IT, centrality, and path analysis.
Beyond IT — Operational technology (OT/IoT), workforce identity and access, and vendor/third-party graphs.
Asset inventory — Connectors and discovery, enriched with financial and ownership data per asset.
Attack Simulation
Run the breach before an attacker does.
Probabilistic engine — Agent-based + discrete-event + Monte Carlo, with attacker and defender agents producing outcome distributions.
After-action analysis — Single points of failure, weak points, degradations, and an overall resilience score.
Adoption simulator — Model what introducing new IT or OT does to performance, security, compliance, and ROI.
Direction — Heading toward continuous, multi-scenario simulation running 24/7.
Financial-Impact Decisioning
Decisions ranked by dollar impact, not severity color.
Impact-first prioritization — Findings and actions are ranked by their effect on value at risk, so the highest-dollar exposures surface first.
Onek.ai Assist — A bring-your-own-AI assistant explains the why and drafts the plan — you stay in control.
Direction — Heading toward autonomous decisioning with financial impact as the primary signal.
Remediation Execution
Close the loop — fast, but controlled.
Approval-gated automation — Risk-scored remediation previews routed through approvals before anything runs.
Runbooks & infrastructure-as-code — Execute within policy guardrails, with a full hash-chained audit trail of every change.
Direction — Heading toward mostly autonomous execution, with humans on high-severity actions only.
Governance & Compliance
Stay audit-ready as the model changes.
NIST 800-171 — A catalog of 110 controls across 14 families with evidence-backed self-assessment.
CMMC preparedness — Gap analysis and POA&M candidates, mapping your live environment to control status.
Configuration compliance — Golden-config and benchmark policies (CIS, PCI DSS, NIST) evaluated against real device configuration — every failing line, on every asset.
Access review — Every grant from your identity provider against the access actually used: dormant privileges, shadow access, over-exposed assets.
How does Onek.ai work?
From telemetry to a quantified, prioritized decision — in four steps.
Onek.ai works in four steps. (1) Connect telemetry via push streaming or pull collectors (REST, SSH, SNMP, osquery) plus read-only business connectors. (2) Model your environment as a continuously updated digital twin of systems, people, access, data flows, and financial exposure. (3) Simulate probabilistic attacks and technology adoption. (4) Decide and remediate — quantify risk in dollars, check compliance, and close the loop with approval-gated automation.
Connect
Ingest telemetry through push (NiFi-style streaming) or pull collectors (REST, SSH, SNMP, osquery), plus read-only governance connectors for your business systems.
Model
Onek.ai assembles a continuously updated digital twin: systems, people, access, data flows, and financial exposure.
Simulate
Run probabilistic attack and adoption simulations to surface weaknesses, blast radius, and resilience scores.
Decide & remediate
Quantify risk in dollars, check compliance, and close the loop with approval-gated, policy-guarded automation.
Who is Onek.ai for?
From the practitioners managing the environment to the leaders accountable for it.
For Security Leaders
Stop guessing at exposure. See blast radius and single points of failure before an incident, quantify breach cost in dollars, and walk into the board meeting with a defensible risk number and a prioritized remediation plan.
For IT & Infrastructure Teams
One living map of everything you run — assets, networks, access, dependencies — fed by real telemetry. Spot shadow IT and anomalies, trace what connects to what, and push fixes through guided, approval-gated automation.
For Executives & the Board
Cyber risk translated into business terms: value at risk, loss distributions, ROI on proposed technology, and governance posture. Decisions backed by models, not vibes.
For CFOs & Risk Committees
Cyber exposure as a line item: value at risk, loss distributions, and the financial case for each control — expressed in the same language as the rest of enterprise risk.
From curious to running Onek.ai in three steps
Enterprise software shouldn't hide how you buy it. Here is exactly what working with us looks like — and how long each step takes.
Explore the live demo
Right now · self-serve
Open the full platform on a seeded enterprise environment. Break something in the twin, read the dollar figure, see who can reach what, export the board report.
- No signup, no sales call
- Every feature unlocked
- Same build we ship to customers
Guided walkthrough
30 minutes · with the founding team
Bring your real questions — board reporting, a pending CMMC assessment, an M&A target — and we drive the platform against them.
- Your scenarios, our model
- Architecture & deployment Q&A
- Candid fit assessment
Pilot in your environment
Weeks, not quarters
Self-hosted in your infrastructure — Docker Compose today, Kubernetes manifests on request — fed by your telemetry. We agree the success criteria up front and report against them, in writing.
- Read-only connectors, your data stays home
- Dollar-denominated findings in the first weeks
- Founding-customer terms for 2026 pilots
Pricing is scoped per environment (asset count, deployment model, support tier) and shared in the walkthrough — no procurement maze, no surprise line items.
How does Onek.ai keep enterprise data secure?
A security model, deployment story, and AI approach designed for environments where the stakes are real.
Onek.ai is built for enterprise trust: role- and attribute-based access control, privileged access management, and a hash-chained, tamper-evident audit log. Single sign-on uses OIDC (PKCE, JWKS, RS256, claim validation), with SAML on the roadmap. Privacy-preserving analysis runs server-side, so raw sensitive data never reaches the client. Deploy via Docker/Compose and bring your own AI provider.
Enterprise security model
Role- and attribute-based access control, privileged access management, and a hash-chained audit log.
Single sign-on
OIDC login with PKCE, JWKS, RS256, and claim validation. SAML support is on the roadmap.
Privacy-preserving analysis
PII classification, pseudonymization, k-anonymity, and differential privacy run server-side; raw sensitive data never reaches the client.
Deploy your way
Containerized stack (Docker / Compose) with a documented go-live runbook.
Bring your own AI
Your models, your keys, encrypted at rest.
Onek.ai vs. traditional security tools
How a unified digital twin compares to the stitched-together stack most teams run today.
| Capability | Traditional stack | Onek.ai |
|---|---|---|
| Environment model | Static diagrams, periodic snapshots | Live digital twin from real telemetry |
| Network mapping | Manual, quickly outdated | Live map reacting to observed traffic |
| Attack testing | Point-in-time pen tests | Continuous probabilistic attack simulation |
| Risk expression | Red/yellow/green heat maps | Value at Risk in dollars + loss distribution |
| Prioritization | Severity scores, gut feel | Business impact & blast radius |
| Compliance | Separate GRC binder, attested once a year | NIST 800-171 / CMMC built in; policies evaluated against live config |
| Access review | Quarterly spreadsheet of grants | Granted vs. actually used — dormant and shadow access, continuously |
| Remediation | Disconnected ticket backlog | Approval-gated, policy-guarded automation |
| Sources of truth | 5+ tools that disagree | One unified model |
“Traditional stack” refers to a typical combination of SIEM, attack surface management, GRC tooling, and spreadsheets.
What sets Onek.ai apart
Risk in dollars, not heat maps — Quantitative VaR and Monte Carlo loss distributions express exposure in money — the language the board and CFO already use.
Decisions ranked by financial impact — Findings and fixes are prioritized by their effect on value at risk, so the highest-dollar exposures rise to the top first.
One platform, not five tools — Inventory, mapping, simulation, risk, remediation, and compliance on a single model — instead of five tools that disagree.
A twin that's actually live — Driven by real telemetry across IT, OT, people, and third parties, with a map that reacts to traffic in real time.
Simulate before you spend — Test attacks and new technology against your real environment before committing budget.
Open by design — Bring your own AI provider; deploy in your own infrastructure.
Built for where cyber risk is heading
The center of gravity is shifting from security tooling to financial-risk decisioning. Here is what Onek.ai does today — and where each capability is going.
The “Today” column reflects shipped capability. The “Direction” column is our roadmap, not a current claim.
What is a digital twin for cybersecurity?
A digital twin for cybersecurity is a continuously updated, virtual model of an organization's IT environment — its systems, users, access paths, data flows, and dependencies — built from live telemetry. Unlike a static network diagram, it stays in sync with reality, so teams can simulate attacks, measure blast radius, and quantify risk against the actual environment. Onek.ai is a digital twin security platform built on this model.
How it differs from related tools
- vs. SIEMA SIEM collects and correlates logs after events; a digital twin maintains a live structural model you can simulate against.
- vs. attack surface management (ASM)ASM inventories external exposure; a digital twin models internal topology, blast radius, and business impact.
- vs. a CMDBA CMDB is a configuration record; a digital twin is a behavioral, simulatable model enriched with risk and financial data.
Cyber risk by the numbers
The case for quantifying and consolidating cyber risk.
20%
Of breaches used vulnerability exploitation for initial access — up 34% year over year
Verizon Data Breach Investigations Report, 2025Sources are linked per figure and updated annually. Onek.ai-specific outcome metrics will be added once measured.
Built on standards you already trust
Onek.ai is engineered for environments where the stakes are real — grounded in recognized security and compliance frameworks, and designed to run inside your own infrastructure.
We are onboarding a small number of design partners this year.
Design partners run Onek.ai against their own environment in a structured pilot, get direct access to the founding team, shape the roadmap, and lock in founding-customer terms.
Frequently asked questions
Straight answers on digital twins, cyber risk quantification, and how Onek.ai works.
A continuously updated virtual model of your IT environment — systems, users, access, data flows, and dependencies — built from live telemetry. It stays in sync with reality so you can simulate attacks, measure blast radius, and quantify risk against your actual environment rather than a static diagram.
Still have questions? hello@onek.ai
Put a number on it.
Security has always been the budget line nobody could measure. Onek.ai turns it into a figure you can defend, track and improve quarter over quarter. Open the demo now, or bring your own questions to a 30-minute walkthrough.